• Latest

GitLab Patches Critical 12-Year Remote Code Execution Flaw Affecting All Versions Since 2014

October 22, 2026

Smart TVs Send Data Even After Users Opt Out, Research Finds

October 22, 2026

North Korea to Resume Border Propaganda Loudspeakers Amid Rising Tensions

October 22, 2026

Global Timekeepers Move Toward Redefining the Second and Replacing Leap Second

October 22, 2026

Japan launches mission to collect samples from Mars’ moon Phobos

October 22, 2026

One killed, eight injured in attack on Saudi Arabia’s King Fahd airport

October 22, 2026

US Orders Departure of Some Diplomats from Saudi Arabia After Houthi Attacks

October 21, 2026

Disrupted Body Clocks Linked to One in Four Depression Cases, Study Finds

October 21, 2026

AMD Rolls Out FSR 4.1 to RX 6000 GPUs and Handhelds, Xbox Update Pending

October 21, 2026

DC Studios Confirms Batman Is Active in Gotham During ‘Clayface’ Events

October 21, 2026

Apple Music launches new sound-inspired logo and visual identity

October 21, 2026

Study Links Higher Daily Step Counts to Sharper Cognitive Performance

October 21, 2026

Cyberpunk 2077 Update 2.5 Adds New Story Quests, Gear, and Gameplay Features

October 21, 2026
Picupnews
  • Home
  • News
  • Tech
  • Entertainment
  • Lifestyle
No Result
View All Result
  • Home
  • News
  • Tech
  • Entertainment
  • Lifestyle
No Result
View All Result
No Result
View All Result
Picupnews
  • Home
  • News
  • Tech
  • Entertainment
  • Lifestyle
Home Latest

GitLab Patches Critical 12-Year Remote Code Execution Flaw Affecting All Versions Since 2014

October 22, 2026
in Latest, Tech
Share on TwitterShare on Facebook

GitLab has released emergency security patches to address a critical vulnerability that could allow unauthenticated attackers to execute arbitrary code on self-managed servers. The flaw, tracked as CVE-2026-110264 and rated the maximum 10.0 on the CVSS severity scale, affects all GitLab Community and Enterprise Edition releases since version 7.0, first launched in 2014. The company urges administrators to update immediately, as the issue exposes servers to complete compromise.

According to official GitLab documentation and multiple cybersecurity news outlets, the vulnerability is rooted in Ruby’s built-in regular expression engine, Onigmo, which is bundled and patched by GitLab in its own software packages. The flaw arises from an integer overflow that occurs when the engine compiles a specially crafted regular expression, potentially enabling remote code execution without authentication.

The patches were made available on October 21, following the discovery and responsible disclosure of the issue through GitLab’s bug bounty program. GitLab has not detailed the exact conditions required for an attacker to exploit the vulnerability, but security experts emphasize that the risk is severe due to the unauthenticated nature of the attack and the wide range of affected versions.

Administrators who previously applied GitLab’s October 12 security update are being told they must upgrade again, as the new releases supersede those earlier patches. The company has confirmed that only self-managed GitLab instances are vulnerable; GitLab.com and GitLab Dedicated environments are not affected by this flaw.

This latest incident comes amid a series of critical vulnerabilities disclosed in GitLab products over recent weeks, including another CVSS 10.0 unauthenticated code execution bug fixed earlier this month. The repeated emergence of high-severity flaws in the platform’s regular expression processing highlights the ongoing challenges in securing complex development toolchains.

Security researchers note that no interim workaround is available for CVE-2026-110264. Applying the official patches is the only reliable method to mitigate the risk. GitLab has published a list of fixed versions, including 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, and 18.11.13, and urges all users to upgrade as soon as possible.

There is no evidence yet of active exploitation in the wild, but the lack of detailed technical barriers and the criticality of the flaw have prompted urgent warnings from the cybersecurity community. Administrators are advised to review their deployments and apply updates without delay.

It remains unclear whether all installations are equally exposed, as GitLab has withheld specifics on the conditions required to trigger the vulnerability. However, experts agree that the safest approach is to assume exposure and patch immediately. Further information may be released as investigations continue and as researchers analyze the patched code.

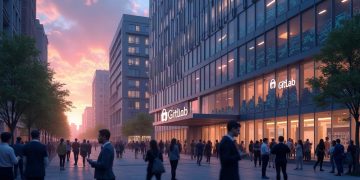
The image accompanying this article is an AI-generated illustrative depiction inspired by the actual scene of the event.
Tags: CVE-2026-110264CybersecurityGitLabRemote Code Execution
Previous Post

North Korea to Resume Border Propaganda Loudspeakers Amid Rising Tensions

Next Post

Smart TVs Send Data Even After Users Opt Out, Research Finds

Related Posts

Smart TVs Send Data Even After Users Opt Out, Research Finds

October 22, 2026

Smart TVs from major brands are continuing to send user data to tracking endpoints even after users have opted out...

North Korea to Resume Border Propaganda Loudspeakers Amid Rising Tensions

October 22, 2026

North Korea is preparing to restart anti-South Korea propaganda broadcasts along the heavily fortified border, with officials in Pyongyang saying...

Global Timekeepers Move Toward Redefining the Second and Replacing Leap Second

October 22, 2026

International timekeeping authorities are preparing for a major overhaul of how the world measures time, with discussions underway to redefine...

Japan launches mission to collect samples from Mars’ moon Phobos

October 22, 2026

Japan has launched a groundbreaking mission to collect rock and dust samples from Phobos, one of Mars’ two moons, aiming...

One killed, eight injured in attack on Saudi Arabia’s King Fahd airport

October 22, 2026

One person was killed and eight others injured in an attack on King Fahd International Airport in Dammam, eastern Saudi...

US Orders Departure of Some Diplomats from Saudi Arabia After Houthi Attacks

October 21, 2026

The US State Department has ordered the departure of some diplomatic personnel and their families from Saudi Arabia, following a...

Next Post

Smart TVs Send Data Even After Users Opt Out, Research Finds

  • Trending
  • Comments
  • Latest
North Korean Soldiers in Russia: A New Twist in the Ukraine War

North Korean Soldiers in Russia: A New Twist in the Ukraine War

November 26, 2024
UN Human Rights Council Calls for Electoral Transparency in Venezuela

UN Human Rights Council Calls for Electoral Transparency in Venezuela

December 4, 2024
Netanyahu and Gallant: Facing Arrest Warrants from the ICC

Netanyahu and Gallant: Facing Arrest Warrants from the ICC

November 26, 2024
Is TikTok Being Banned in the US? A Federal Court Decision Sparks Uncertainty

Is TikTok Being Banned in the US? A Federal Court Decision Sparks Uncertainty

December 6, 2024
Russia-Ukraine War: A Conflict That Shakes Global Balance

Russia-Ukraine War: A Conflict That Shakes Global Balance

Hubble Space Telescope Reveals Surprising Details About FU Orionis

Hubble Space Telescope Reveals Surprising Details About FU Orionis

Huawei Takes a Bold Step Toward Technological Independence with HarmonyOS Next

Huawei Takes a Bold Step Toward Technological Independence with HarmonyOS Next

Donald Trump’s Return: What It Means for Big Tech and Emerging Technologies

Donald Trump’s Return: What It Means for Big Tech and Emerging Technologies

Smart TVs Send Data Even After Users Opt Out, Research Finds

October 22, 2026

GitLab Patches Critical 12-Year Remote Code Execution Flaw Affecting All Versions Since 2014

October 22, 2026

North Korea to Resume Border Propaganda Loudspeakers Amid Rising Tensions

October 22, 2026

Global Timekeepers Move Toward Redefining the Second and Replacing Leap Second

October 22, 2026

Recent News

Smart TVs Send Data Even After Users Opt Out, Research Finds

October 22, 2026

GitLab Patches Critical 12-Year Remote Code Execution Flaw Affecting All Versions Since 2014

October 22, 2026

North Korea to Resume Border Propaganda Loudspeakers Amid Rising Tensions

October 22, 2026

Global Timekeepers Move Toward Redefining the Second and Replacing Leap Second

October 22, 2026
Picupnews

As a next-generation news agency, we are here to deliver the most important summaries from the global agenda quickly and impartially. Follow us for the latest updates and stay connected to the news!

Follow Us

Browse by Category

  • Business
  • Economy
  • Entertainment
  • Fashion
  • Gaming
  • Health
  • Latest
  • Lifestyle
  • Mobile
  • Movie
  • Music
  • News
  • Politics
  • Science
  • Tech
  • Travel
  • World

Recent News

Smart TVs Send Data Even After Users Opt Out, Research Finds

October 22, 2026

GitLab Patches Critical 12-Year Remote Code Execution Flaw Affecting All Versions Since 2014

October 22, 2026
  • Contact
  • Privacy & Policy
  • Türkçe

© 2026 Picupnews. All rights reserved. · About · Privacy and Cookie Policy · Contact

No Result
View All Result

© 2026 Picupnews. All rights reserved. · About · Privacy and Cookie Policy · Contact

This website uses cookies to analyse traffic and to show ads. By continuing to use the site, you agree to our use of cookies. Privacy and Cookie Policy
This content is powered by n8n automation. Build your own: Educattech  ·  AI content platform: Ommini